Trusted issuers
Anyone can issue a credential. Whether you should trust it depends on who issued it.
The Trusted issuers screen holds the answer for this wallet. Credentials in your wallet are checked against it, and a credential from an issuer that is not on the list is marked as untrusted.
mdoc credentials are never trusted by default. An mdoc is only trusted once an MDoc trust anchor covers the certificate authority behind it.
All other credentials are trusted by default, but only while nothing is configured. As soon as a trusted issuer list is configured, every non-mdoc credential is checked against it and its issuer must appear on the list.
Open the screen
- Open Settings.
- Under Generic, select Trusted issuers.
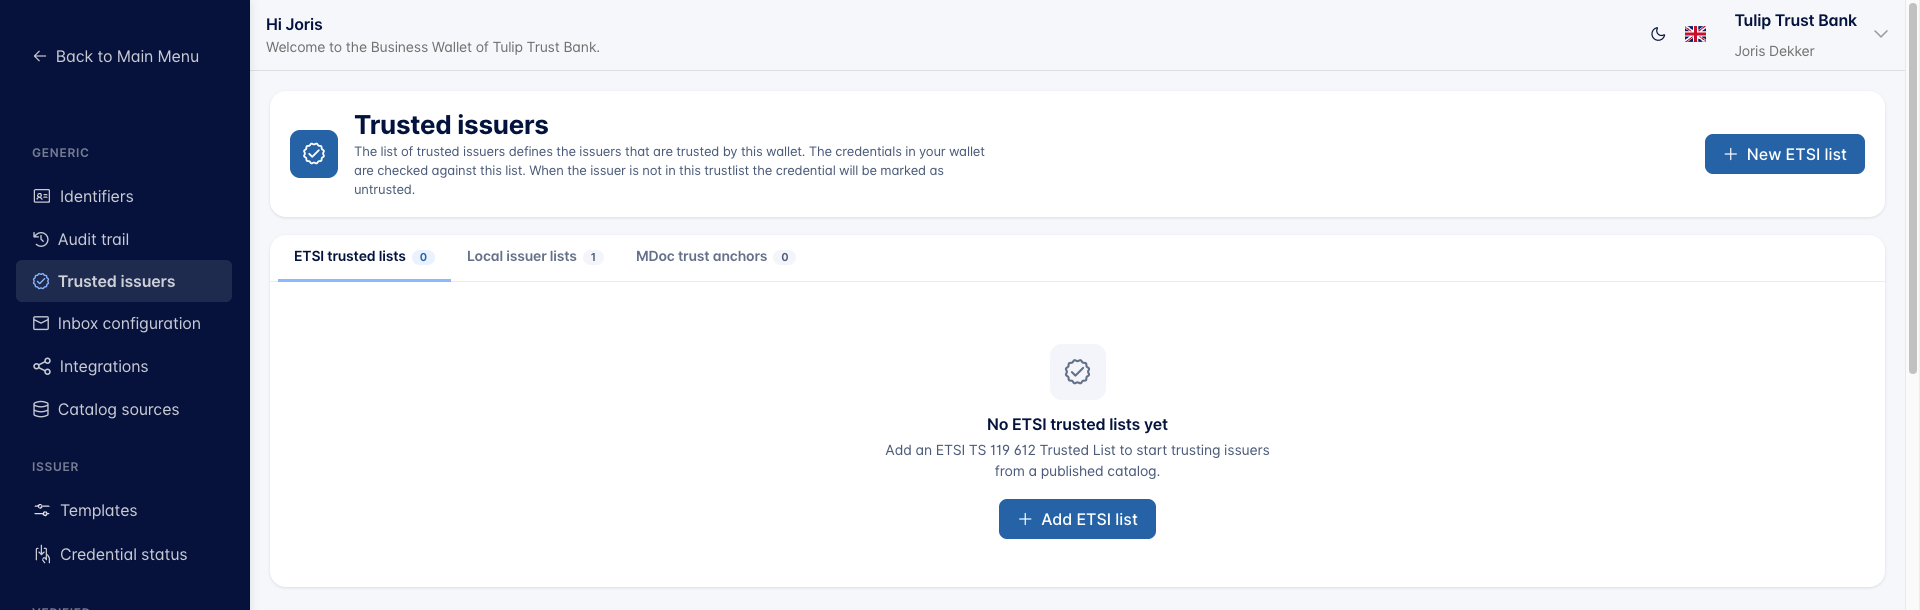
Trust is configured in three places, one per tab. The badge next to each tab name is the number of entries it holds.
- ETSI trusted lists: trust everything on a list somebody else publishes and maintains.
- Local issuer lists: trust a handful of issuers you name yourself, per credential type.
- MDoc trust anchors: trust the certificate authorities behind mdoc credentials.
The button in the top right follows the tab you are on: New ETSI list, New issuer list, or New trust anchor.
ETSI trusted lists
An ETSI TS 119 612 Trusted List is a signed, published catalog of issuers, maintained by a scheme operator such as a national supervisory body. Pointing your wallet at one means you trust every issuer on it, and you stay in step as the operator adds and removes entries.
Click New ETSI list.
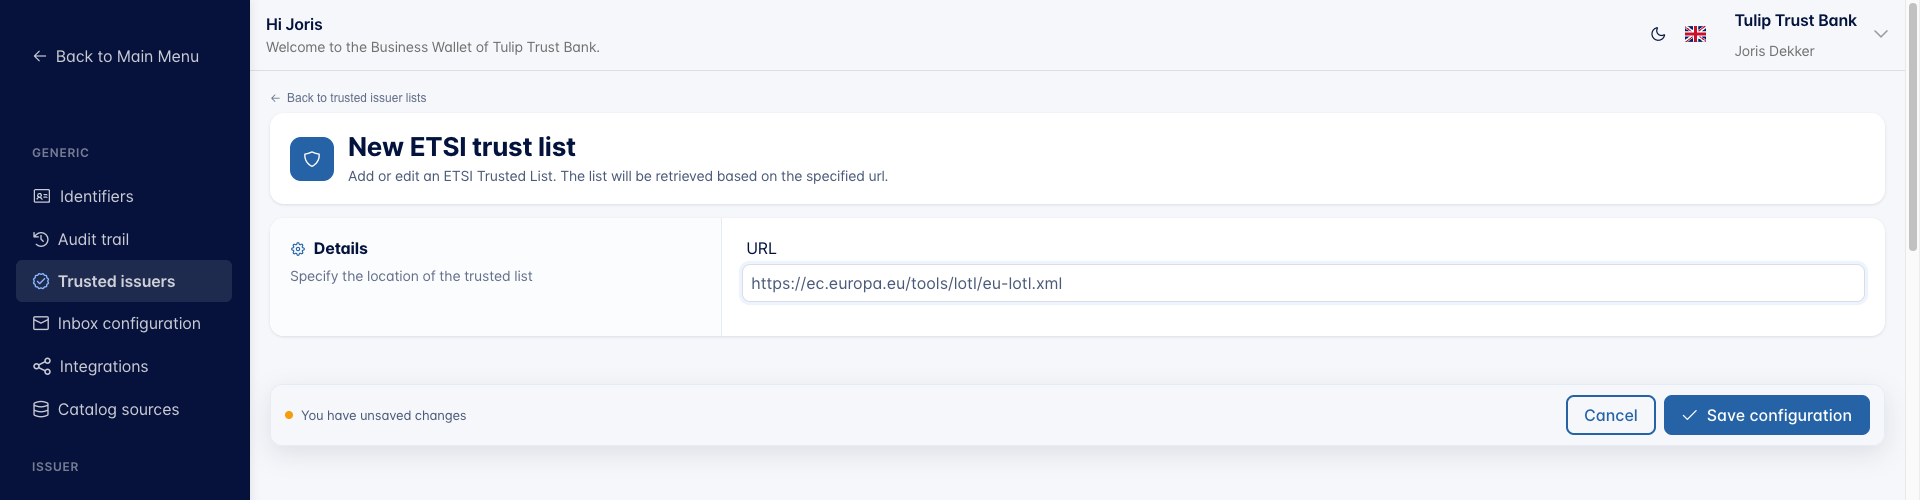
- URL (required): where the trusted list is published. The list itself is fetched from this address, so there is nothing else to fill in.
Click Save configuration to add it. Open an existing list from the table to change its URL or delete it.
Only entries the list publishes as granted attestation services are taken from it.
An ETSI trusted list is not scoped to a credential type: its issuers are trusted for every credential type. Use a local issuer list when you need trust limited to one type.
Local issuer lists
Use a local issuer list when no published list covers your case: you know exactly which issuers you accept, and you want to say so yourself.
Each list is scoped to one credential type, so trusting an issuer for company certificates does not silently trust it for diplomas.
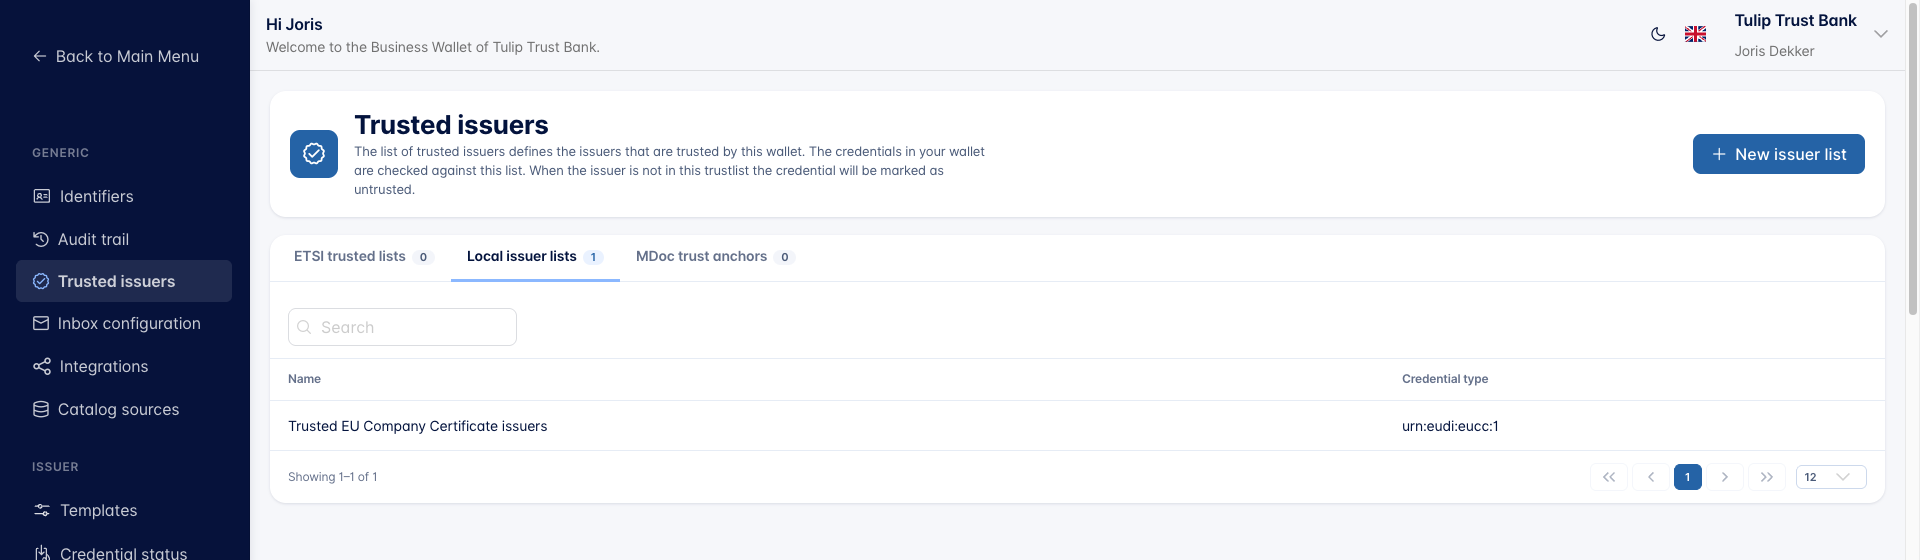
The table shows the Name and the Credential type of each list. Use the Search box to filter it, and click a row to open the list.
Click New issuer list to create one.
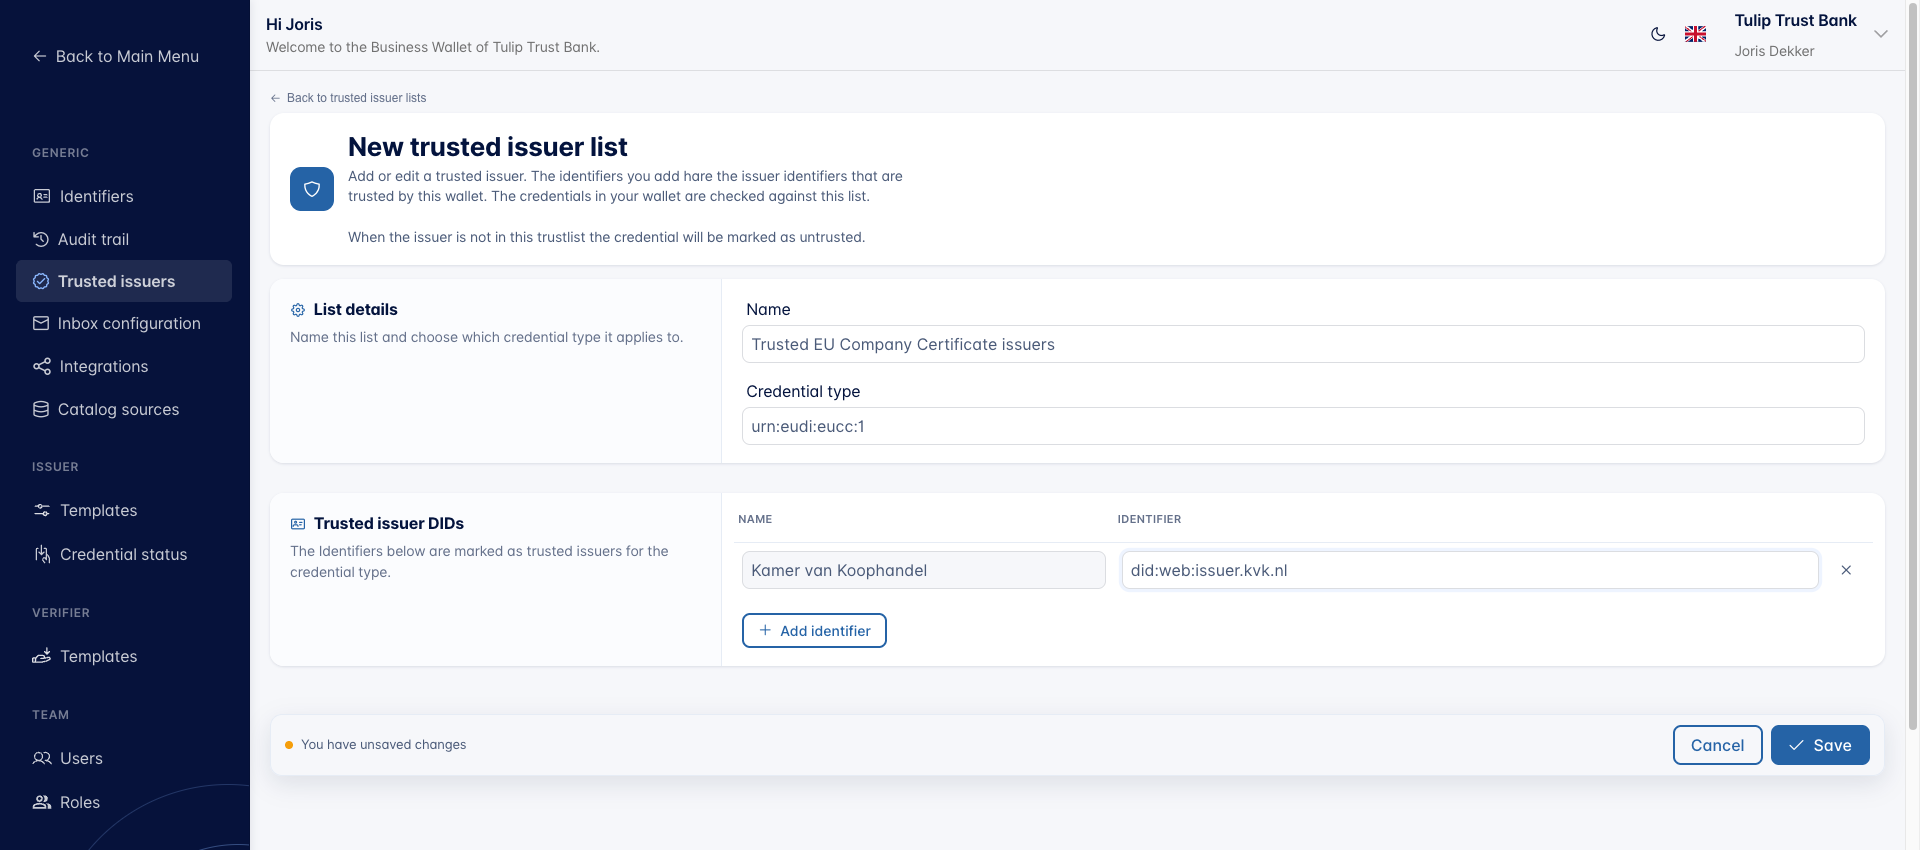
Under List details:
- Name (required): a free format name, for your own use only.
- Credential type (required): the type this list applies to, written exactly as it appears in the credential. For an SD-JWT credential that is its type identifier, for example
urn:eudi:eucc:1. For a JSON-LD or JWT credential it is the last entry of the credential's type, for exampleOprichtingsAkte.
Under Trusted issuer DIDs, click Add identifier for every issuer you want to trust:
- Name: a free format name, so you can tell the identifiers apart.
- Identifier: the identifier (DID) of the issuer, for example
did:web:issuer.kvk.nl.
Use the cross at the end of a row to remove an identifier. Click Save to apply the list.
Open a credential in your wallet and look at its type. That value, copied exactly, is what belongs in Credential type. A mismatch means the list never applies, and the credential stays untrusted.
MDoc trust anchors
Mdoc credentials (ISO 18013-5, the format behind mobile driving licences and similar documents) do not name their issuer with an identifier. They are signed by a document signer, whose certificate chains up to the certificate of an issuing authority: the IACA certificate.
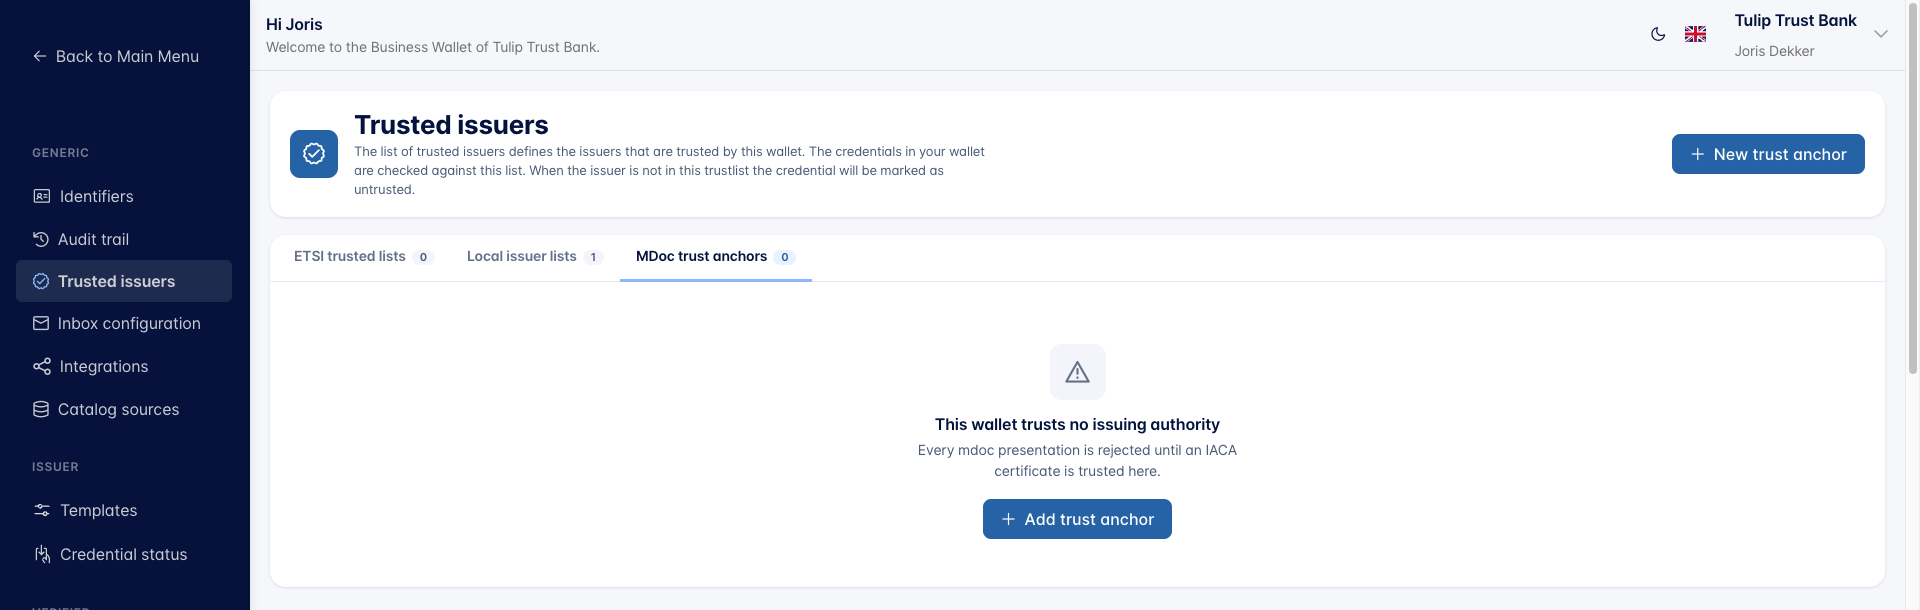
Every mdoc presentation is rejected until an IACA certificate is trusted here. An empty tab is not a neutral setting.
Click New trust anchor.
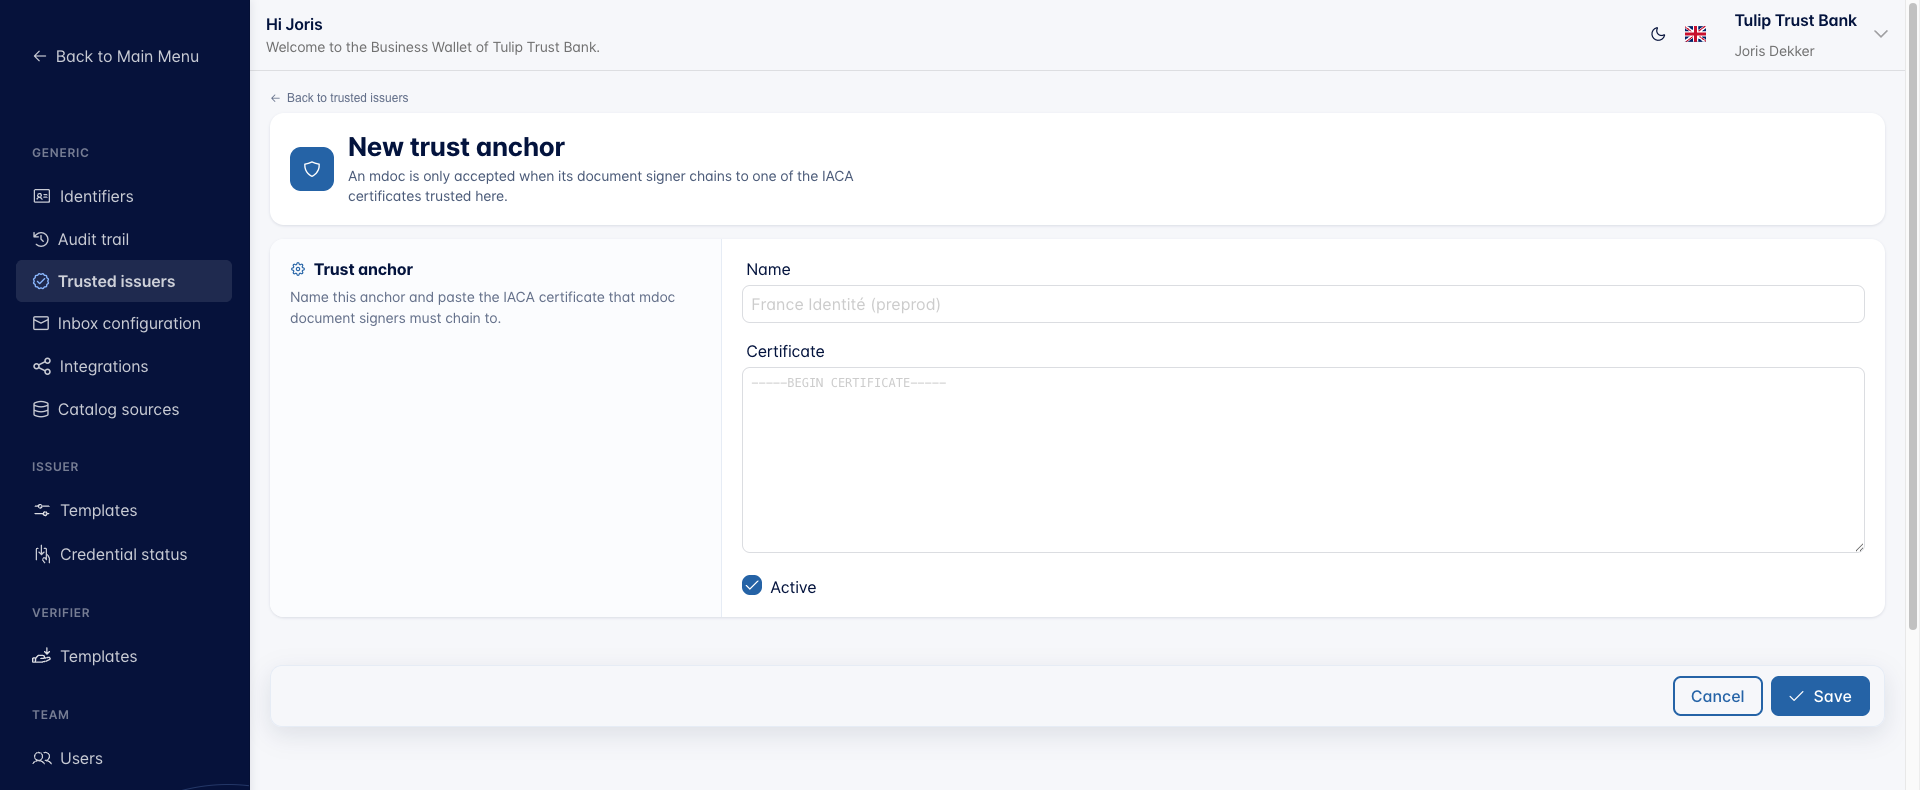
- Name (required): a free format name for the issuing authority, for example
France Identité (preprod). - Certificate (required): the IACA certificate itself, pasted in PEM form, starting with
-----BEGIN CERTIFICATE-----. - Active (on by default): whether this anchor counts. Switch it off to stop trusting an authority without deleting the certificate, which is useful while you are testing.
Click Save to add the anchor.
How the list is used
Trusted issuers are not enforced everywhere by default. A verifier template applies the check only when its Trusted issuer check policy is switched on. See Create Verifier Template for that setting.
You need the Trusted issuers (View) permission to open this screen, and Trusted issuers (Change) to add, edit, or delete entries.